Keep your communications private. Across every site.
Place a HEXACRYPT encryptor between each trusted LAN and the transport network. Your traffic travels encrypted between sites, while your applications continue to operate as usual.
Trusted LANSite A
PLAIN → CIPHER
Encrypt
Encrypted transportFiber · Ethernet · IP / MPLS · Wireless
CIPHER → PLAIN
Decrypt
Trusted LANSite B
01
Application-independent
Protect network traffic at Layers 2 and 3 without modifying individual applications.
02
Dedicated encryption
Separate the encryption layer from the carrier or transport network that connects your sites.
03
One management environment
Provision encryptors, manage keys and supervise the secure network through Crypto DMS.
02 / HEXACRYPT encryptors
Two formats. One secure network.
Choose the capacity and form factor that fit each location, from a branch office to a data centre. Both devices support point-to-point, hub-and-spoke and meshed encrypted networks.
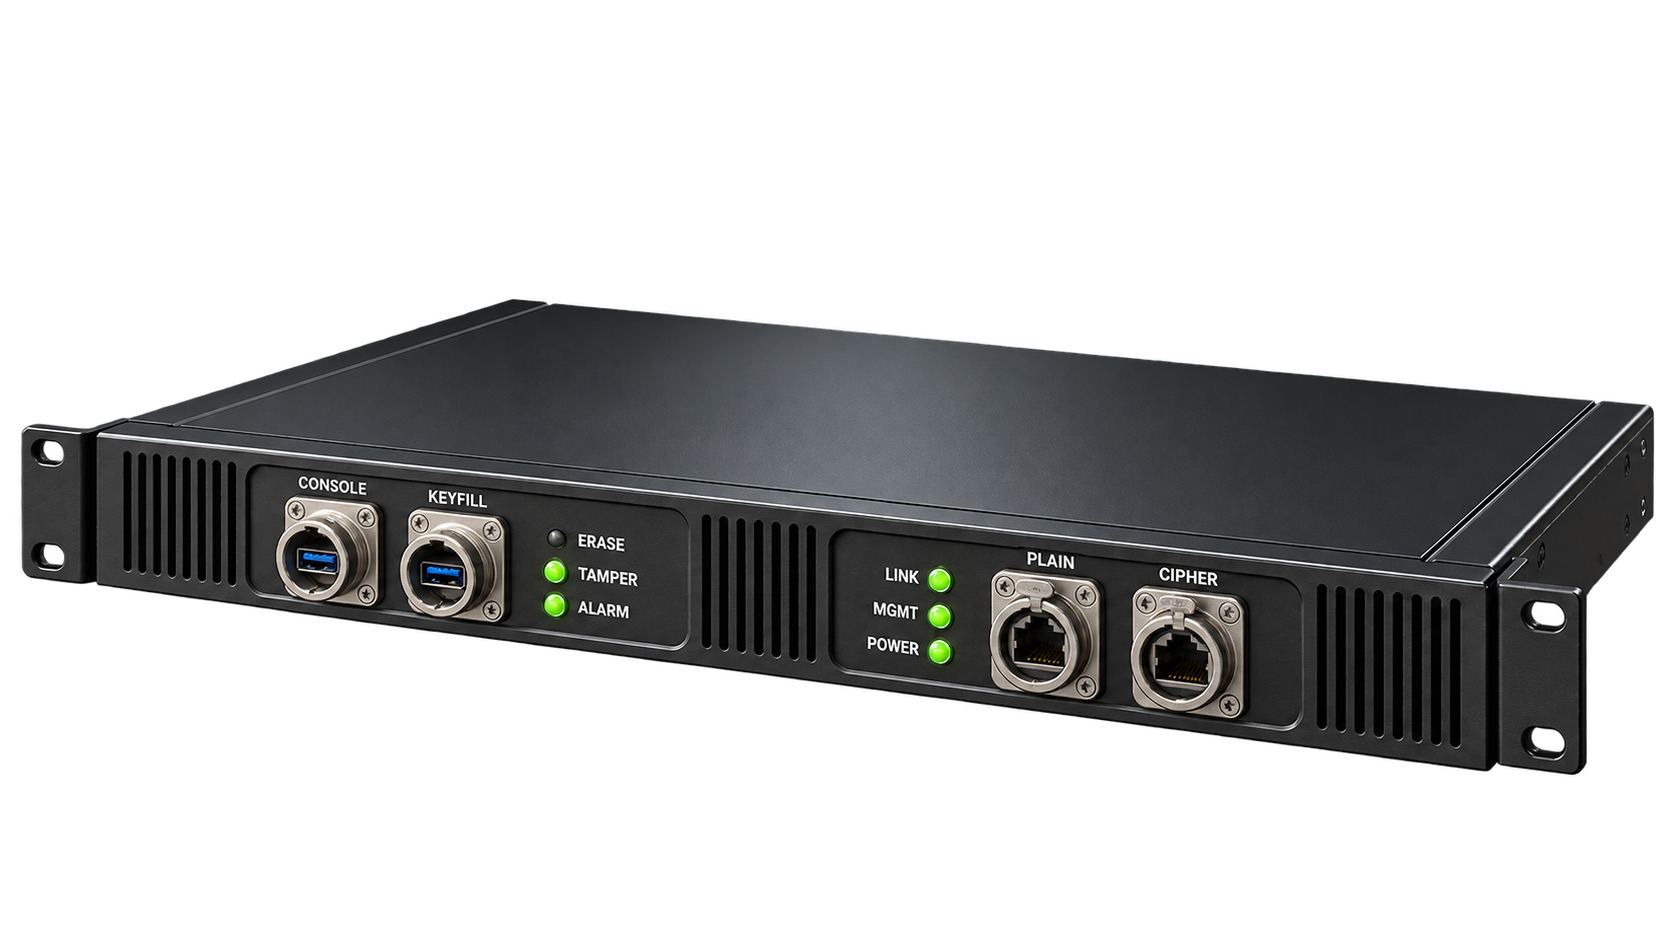
HIGH-PERFORMANCE ENCRYPTION1 Gbps
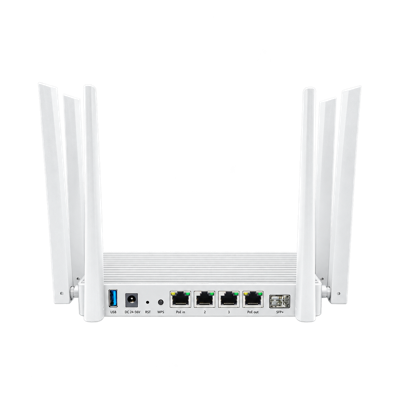
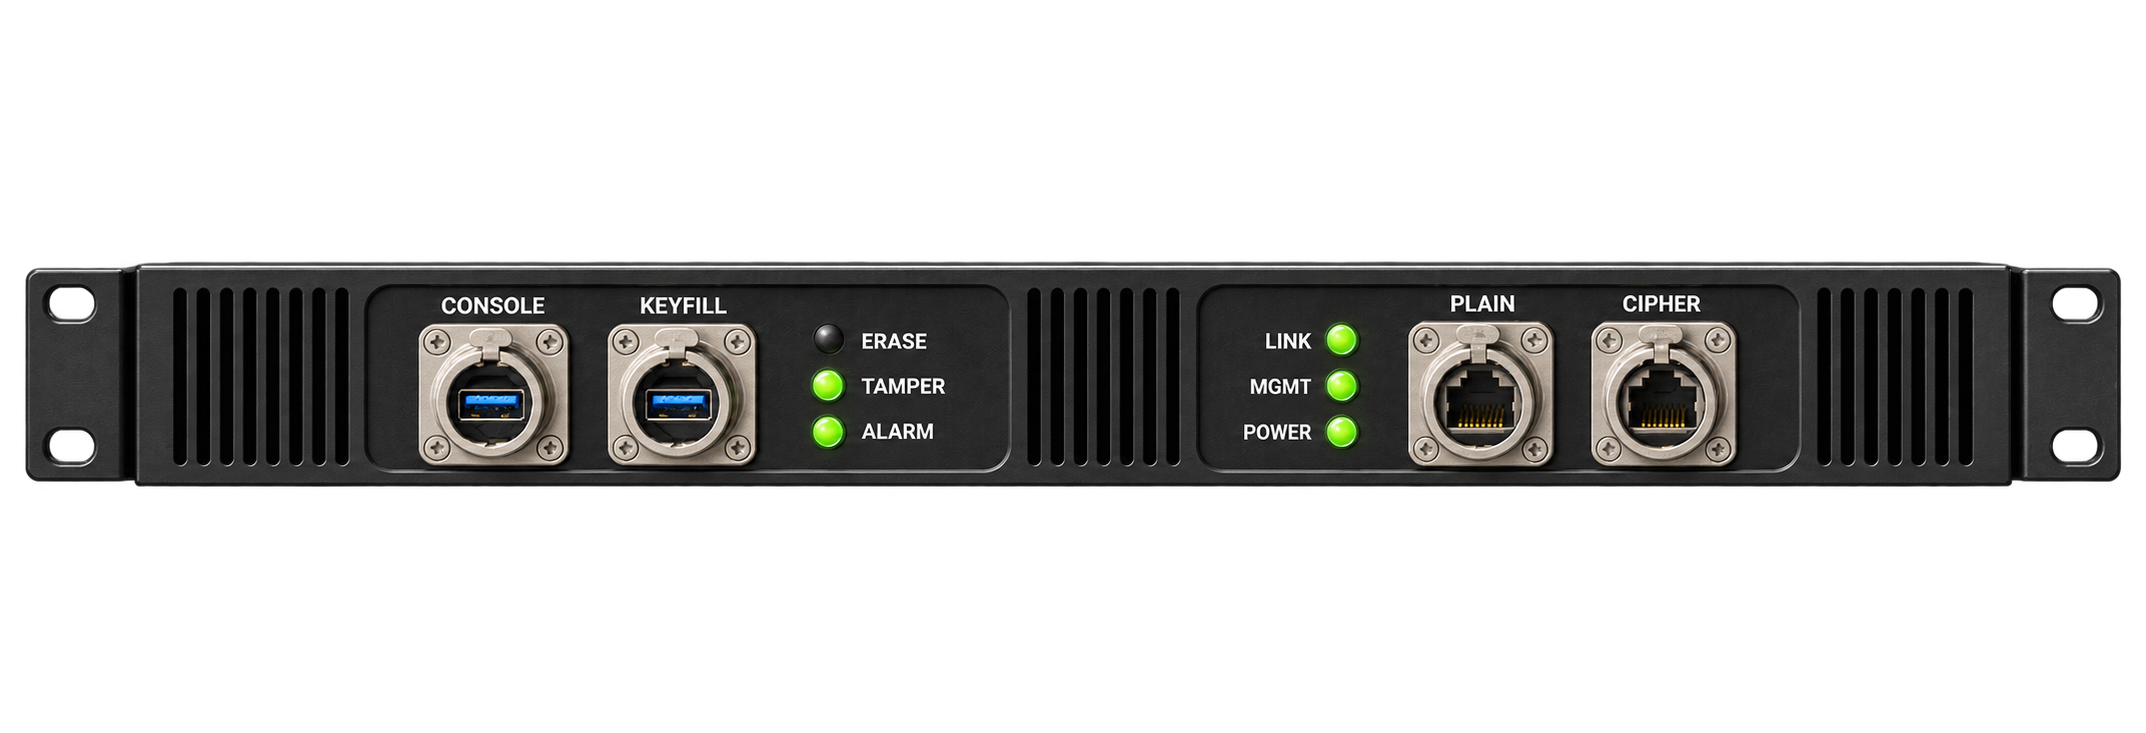
GIGACRYPT
Hardware encryption for headquarters, data centres and critical inter-site links.
Encryption throughput
Up to 1 Gbps bidirectional
Encryption engine
Dedicated FPGA · AES-256-GCM
Format
1U · 19-inch rack mount
Network support
Layers 2 / 3 · IPv4, IPv6 & non-IP traffic
Device management
Crypto DMS · Local CLI
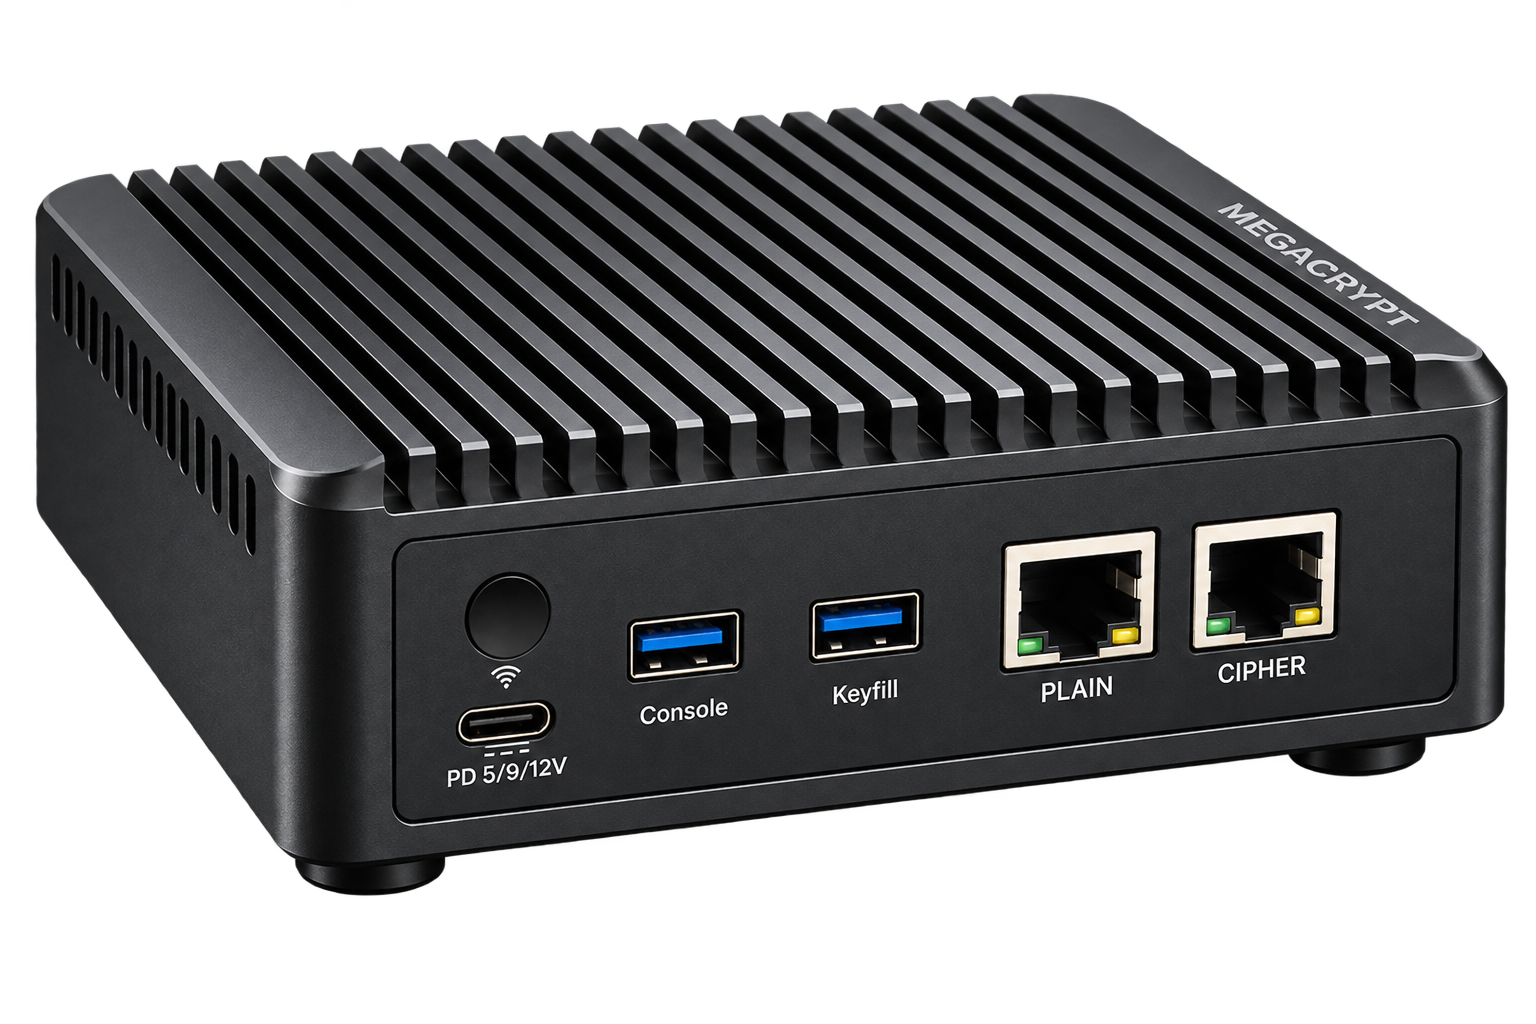
COMPACT SITE ENCRYPTION100 Mbps
COMPACT ENCLOSURE
MEGACRYPT
Compact encryption for branches, agencies and distributed operational sites.
Encryption throughput
100 Mbps bidirectional
Encryption engine
Processor-based encryption
Format
Compact desktop enclosure
Network support
Layers 2 / 3 · IPv4 & IPv6
Device management
Crypto DMS
Build the encryption layer around your topology, traffic and operational requirements.
03 / Crypto device management
Crypto DMS. Control beyond the device.
Bring provisioning, configuration, keys and operational visibility into one environment. Manage your encrypted network from the first site to a distributed infrastructure.
CENTRALIZED MANAGEMENTIllustrative architecture
Encrypted trafficSecure management
The data flows between encryptors. Crypto DMS manages and supervises them.
DEPLOY & CONFIGURE
Bring new sites into your secure network.
Onboard encryptors with zero-touch provisioning, apply configuration templates and define the peers that can communicate.
Device onboarding and configuration
Peer and network topology management
Firmware and configuration operations
FOR YOUR ORGANISATION
Dedicated management
A dedicated DMS environment for your headquarters, data centres, branches and operational sites.
FOR MANAGED SERVICES
Multiple customers. Central operations.
A shared multi-tenant DMS, or a dedicated environment per customer, to match your isolation and operating requirements.
CONNECTED TO YOUR WORKFLOWS
Integrate and automate
Use REST APIs, event notifications and audit trails to connect encryption operations with your wider supervision environment.
04 / Secure network architectures
Designed around the way your sites connect.
Protect your own critical infrastructure or deliver managed encrypted connectivity to customers. Select an architecture to explore a typical deployment.
DATA CENTRE ↔ DISASTER RECOVERY
Protect a critical inter-site link.
Place an encryptor at each end of the transport network to protect communications between two trusted locations, such as a primary data centre and a disaster recovery site.
Tell us about your sites, bandwidth and security requirements. Our experts will help you define the HEXACRYPT equipment and Crypto DMS architecture for your deployment.